

Garda Launches Major Update to Its DDoS Protection Platform
The solution keeps networks operational even during sharp spikes in traffic.
DDoS attacks are among the most common cyber threats facing businesses. Threat actors can suddenly flood an organization’s infrastructure with traffic, potentially causing major system disruptions and even bringing systems and digital services to a complete halt. Attack methods are also becoming increasingly sophisticated, requiring security vendors to continually improve their defenses.
Silicom E810 Support
Recently, Garda, part of IKS Holding, introduced a new version of its Garda Anti-DDoS platform, designed to defend against combined attacks. It helps keep systems running during sharp traffic spikes and failures at protection nodes. The update also simplifies how security teams work with web log analysis rules and expands attack-filtering capabilities.
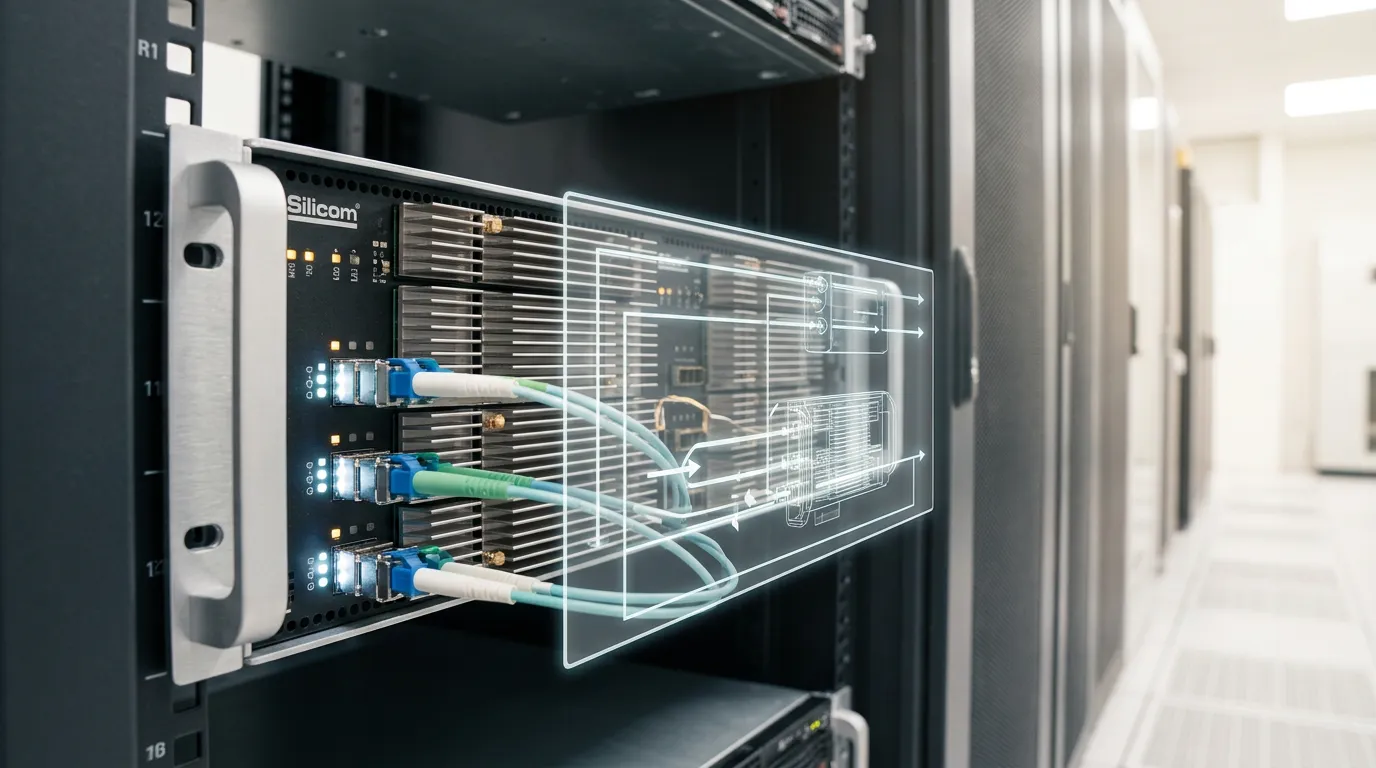
One of the biggest functional additions is support for Silicom E810 network adapters. The platform is now compatible with network cards that deliver data rates of up to 100 Gbps and support hardware bypass. This combination allows the system to handle large volumes of traffic. The bypass mechanism helps keep the network available if the protection node itself fails. The connection continues to operate in transparent mode, so a device failure does not interrupt communications.
Expanded Analysis Capabilities
The developers also upgraded web server log analysis. The system can now automatically decode URL and referrer fields, making it easier to identify malicious signatures. When processing data, Garda Anti-DDoS determines whether a string is encoded and, when necessary, decodes it before matching it against a signature.
The update also adds protection against LAND attacks. Filtering them now requires only enabling the relevant setting, after which the platform automatically drops packets whose source and destination IP addresses match.
The release also includes several other improvements. Users can now authenticate with an SSH key when working through the command line, and the platform supports Astra Linux 1.8 and Debian 12. Administrators can limit the number of requests sent to servers to retrieve or modify data. These settings can be applied to individual users or entire groups.
A Strategic Security Tool
Developments like these are increasingly important as the economy turns more digital. Businesses are becoming more dependent on the stable operation of online services. In this environment, DDoS protection is no longer simply an IT support function – it is part of keeping digital businesses running continuously.
Demand for DDoS protection tools surged in 2022 as attackers stepped up their activity. According to Qrator Labs, the number of DDoS attacks targeting Russian IT systems increased by 73% that year. The attacks hit the Gosuslugi web portal (Public Services), banks, media outlets and other major resources. That same year, TransTeleCom upgraded its DDoS protection service using Perimetr (Perimeter), a Russian security system developed by Garda Technologies. The system later evolved into Garda Anti-DDoS.
The number of attacks targeting enterprise IT infrastructure continued to rise in the following years. Across the cybersecurity industry, a common development path has been to combine automated filtering with higher infrastructure performance.
Demand for Automation
Security professionals now point to three requirements that are increasingly shaping the development of Anti-DDoS systems: high throughput, multilayer filtering and as few manual operations as possible. Human operators can no longer respond to every threat manually, making automation the only practical way forward.
The latest Garda Anti-DDoS update shows that developers are no longer focused solely on adding more tools for filtering malicious data. The priority now is to make the entire protection chain resilient, and Russian security professionals have the technological expertise needed to build that resilience.